You must be logged in to post a review.
Denial of Service DOS & Distributed Denial of Service DDOS Attacks
This in-depth online course is designed to equip learners with practical knowledge of DoS and DDoS threats, service availability, detection, defensive controls, mitigation, incident response, and resilience planning. By combining foundational cybersecurity concepts with realistic scenarios and defensive best practices, the course provides a structured foundation for understanding availability-related security risks.
KWD 39 Original price was: KWD 39.KWD 25Current price is: KWD 25.
Course Curriculum
1. Introduction to Denial of Service DOS & Distributed Denial of Service DDOS Attacks
- Understanding Denial of Service (DoS) and Distributed Denial of Service (DDoS) attacks.
- Understanding the importance of service availability in cybersecurity.
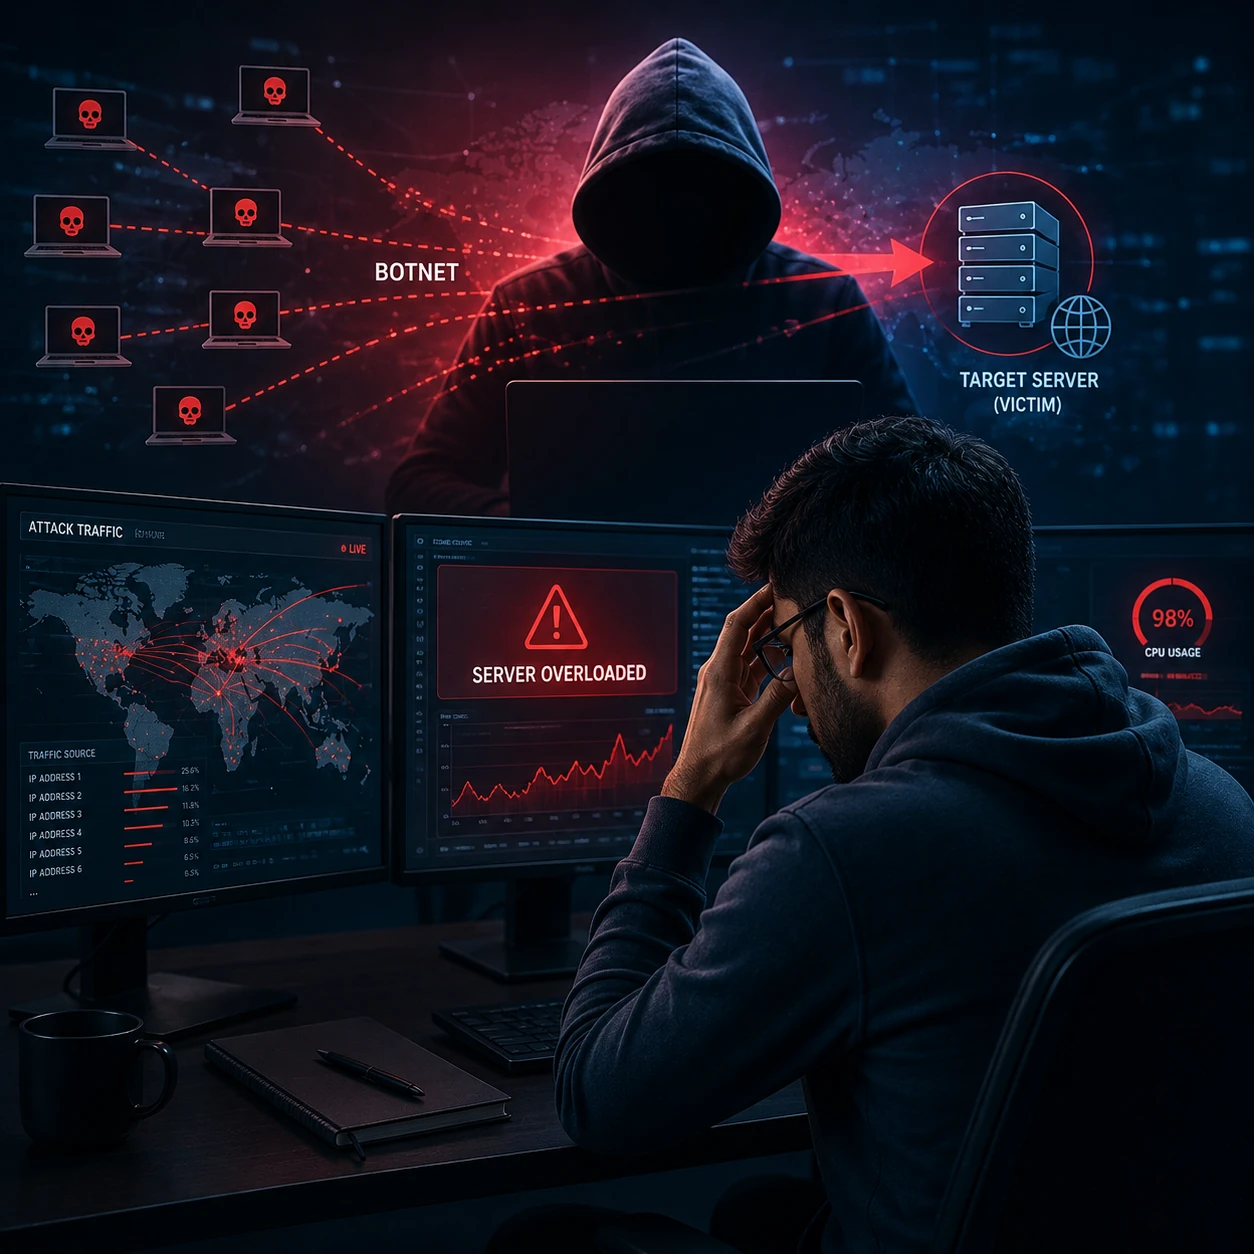
- Differences between DoS and DDoS attacks.
- Common reasons attackers attempt to disrupt online services.
- Understanding the potential impact of availability-based security incidents.
- Introduction to defensive cybersecurity principles.
2. Networking and Service Availability Fundamentals
- Understanding basic computer networking concepts.
- Exploring clients, servers, networks, and internet services.
- Understanding bandwidth, processing capacity, and connection resources.
- Exploring how applications depend on network infrastructure.
- Understanding availability as part of the CIA triad.
- Recognizing common causes of service disruption.
3. Understanding DoS and DDoS Attack Concepts
- Exploring how denial-of-service conditions can affect services.
- Understanding traffic overload and resource exhaustion at a conceptual level.
- Comparing centralized and distributed sources of unwanted traffic.
- Understanding the role of compromised devices in distributed threats.
- Recognizing application, network, and infrastructure availability risks.
- Reviewing common indicators of denial-of-service activity.
4. DDoS Attack Types and Threat Characteristics
- Understanding major categories of denial-of-service activity.
- Exploring volumetric attacks conceptually.
- Understanding protocol and network-layer availability risks.
- Exploring application-layer disruption.
- Recognizing differences in traffic patterns and attack characteristics.
- Understanding why different services require different defensive strategies.
5. Detection, Monitoring and Incident Identification
- Recognizing unusual network and application traffic.
- Understanding baseline traffic and normal service behavior.
- Using monitoring concepts to identify availability problems.
- Understanding logs, alerts, and security events.
- Distinguishing legitimate traffic spikes from suspicious activity.
- Developing an incident-identification mindset.
6. DoS and DDoS Prevention and Mitigation
- Understanding layered approaches to availability protection.
- Exploring traffic filtering and rate-limiting concepts.
- Understanding firewalls, load balancing, and network protection.
- Exploring content delivery and distributed infrastructure concepts.
- Understanding redundancy and scalable architecture.
- Developing basic defensive response strategies.
7. Incident Response and Business Continuity
- Understanding the stages of a denial-of-service incident response.
- Establishing communication and escalation procedures.
- Protecting critical services during availability incidents.
- Understanding recovery and service restoration.
- Documenting incidents and reviewing lessons learned.
- Integrating availability threats into business continuity planning.
8. Security Best Practices and Risk Management
- Conducting basic availability-focused security assessments.
- Identifying critical systems and services.
- Understanding third-party and cloud infrastructure considerations.
- Reviewing organizational security policies.
- Improving resilience through layered security controls.
- Promoting security awareness and preparedness.
9. Real-World Implementation
- Denial of Service DOS & Distributed Denial of Service DDOS Attacks case studies
- Industry best practices
- Practical DoS and DDoS detection, risk assessment, monitoring, mitigation, incident response, and service resilience exercises
Certification
After successfully completing the Denial of Service DOS & Distributed Denial of Service DDOS Attacks course, learners can receive a professional course completion certification. The certification demonstrates your commitment to developing knowledge of denial-of-service concepts, network availability, threat detection, defensive security, mitigation strategies, incident response, and cybersecurity risk management.
SEO Introduction
Denial of Service DOS & Distributed Denial of Service DDOS Attacks course is a comprehensive online training program designed to develop an understanding of denial-of-service threats and their impact on digital services. The course explores DoS and DDoS concepts, networking fundamentals, attack characteristics, monitoring, detection, mitigation, incident response, and security best practices.
You will explore the core principles of Denial of Service DOS & Distributed Denial of Service DDOS Attacks, including service availability, network resources, traffic patterns, resource exhaustion, centralized and distributed threats, and common indicators of availability-related security incidents. These concepts can help learners recognize why resilient infrastructure and effective security controls are important.
The course also covers advanced Denial of Service DOS & Distributed Denial of Service DDOS Attacks concepts, including traffic monitoring, filtering, rate limiting, load balancing, layered defenses, infrastructure resilience, incident response, business continuity, and risk management. The course emphasizes defensive and educational approaches to understanding these cybersecurity threats.
By completing the Denial of Service DOS & Distributed Denial of Service DDOS Attacks course, learners can build a stronger foundation in availability-focused cybersecurity. The knowledge gained can be useful for IT professionals, network administrators, cybersecurity learners, students, and organizations seeking to better understand and prepare for service disruption risks.
Requirements
- Basic computer and internet knowledge is recommended.
- Familiarity with basic networking concepts can be helpful but is not essential.
- An interest in cybersecurity, network security, or IT infrastructure is beneficial.
- Learners should be comfortable exploring technical concepts and security terminology.
- Access to a computer and internet connection is recommended for additional learning and research.
Who This Course Is For
- Beginners interested in cybersecurity and network security.
- Aspiring cybersecurity professionals and IT support staff.
- Network administrators and infrastructure professionals.
- Students studying computer science, networking, or information security.
- Professionals who want to understand service availability and denial-of-service risks.
- Anyone interested in defensive approaches to DoS and DDoS threats.
FAQ
1. What is the Denial of Service DOS & Distributed Denial of Service DDOS Attacks course?
It is an online cybersecurity course covering DoS and DDoS concepts, service availability, detection, monitoring, mitigation, incident response, and defensive security practices.
2. What is the difference between DoS and DDoS?
A DoS attack generally involves a single source attempting to disrupt a service, while a DDoS attack involves unwanted traffic or requests originating from multiple distributed sources.
3. Do I need networking experience?
Basic networking knowledge can be helpful, but the course introduces important concepts in an accessible way for learners developing their cybersecurity knowledge.
4. Does the course teach how to launch DDoS attacks?
The course is focused on educational and defensive cybersecurity knowledge. It does not provide instructions for carrying out attacks against real systems or services.
5. Will I learn how to recognize denial-of-service activity?
Yes. The course covers traffic patterns, monitoring, logs, alerts, unusual activity, and other conceptual indicators that can help with recognizing availability-related incidents.
6. Does the course cover DDoS mitigation?
Yes. It introduces defensive concepts including traffic filtering, rate limiting, firewalls, load balancing, distributed infrastructure, redundancy, and layered security controls.
7. Is this course suitable for cybersecurity beginners?
Yes. The course provides foundational knowledge and gradually introduces concepts related to DoS and DDoS threats, detection, mitigation, and incident response.
8. Will I receive a certificate after completing the course?
Yes. Learners can receive a professional course completion certification after successfully completing the course.
KWD 39 Original price was: KWD 39.KWD 25Current price is: KWD 25.
- One Year Access
- Certificate of completion
Reviews
There are no reviews yet.